Top Tips Of Most Up-to-date EX200 Test
High value of EX200 real exam materials and brain dumps for Red-Hat certification for candidates, Real Success Guaranteed with Updated EX200 pdf dumps vce Materials. 100% PASS EX200 Red Hat Certified System Administrator (RHCSA) Exam exam Today!
Free EX200 Demo Online For Red-Hat Certifitcation:
NEW QUESTION 1
CORRECT TEXT
Configure /var/tmp/fstab Permission.
Copy the file /etc/fstab to /var/tmp/fstab. Configure var/tmp/fstab permissions as the following:
Owner of the file /var/tmp/fstab is Root, belongs to group root
File /var/tmp/fstab cannot be executed by any user
User natasha can read and write /var/tmp/fstab
User harry cannot read and write /var/tmp/fstab
All other users (present and future) can read var/tmp/fstab.
Solution:
cp /etc/fstab /var/tmp/
✑ /var/tmp/fstab view the owner setfacl -m u:natasha:rw- /var/tmp/fstab setfacl -m u:haryy:--- /var/tmp/fstab
Use getfacl /var/tmp/fstab to view permissions
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 2
CORRECT TEXT
Notes:
NFS NFS instructor.example.com:/var/ftp/pub/rhel6/dvd
YUM http://instructor.example.com/pub/rhel6/dvd
ldap http//instructor.example.com/pub/EXAMPLE-CA-CERT Install dialog package.
Solution:
yum install dialog
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 3
CORRECT TEXT
Part 1 (on Node1 Server)
Task 10 [Configuring NTP/Time Synchronization]
Configure your system so that it is an NTP client of utility.domain15.example.com
The system time should be set to your (or nearest to you) timezone and ensure NTP sync is configured
Solution:
*
[root@node1 ~]# yum install chrony
[root@node1 ~]# vim /etc/chrony.conf
pool utility.domain15.example.com iburst
[root@node1 ~]# systemctl enable chronyd
[root@node1 ~]# systemctl restart chronyd
[root@node1 ~]# systemctl status chronyd
[root@node1 ~]# tzselect
Please identify a location so that time zone rules can be set correctly.
Please select a continent, ocean, "coord", or "TZ".
1) Africa
2) Americas
3) Antarctica
4) Asia
11) TZ - I want to specify the time zone using the Posix TZ format.
#? 4
*
Please select a country whose clocks agree with yours.
1) Afghanistan 18) Israel 35) Palestine
2) Armenia 19) Japan 36) Philippines
3) Azerbaijan 20) Jordan 37) Qatar
4) Bahrain 21) Kazakhstan 38) Russia
5) Bangladesh 22) Korea (North) 39) Saudi Arabia
#? 5
The following information has been given: Bangladesh
Therefore TZ='Asia/Dhaka' will be used. Is the above information OK?
1) Yes
2) No
#? 1
Asia/Dhaka
[root@node1 ~]# chronyc sources -v
^? utility.domain15.example> 0 7 0 - +0ns[ +0ns] +/- 0ns
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 4
CORRECT TEXT
Add users: user2, user3.
The Additional group of the two users: user2, user3 is the admin group Password: redhat
Solution:
# useradd -G admin user2
# useradd -G admin user3
# passwd user2
redhat
# passwd user3
redhat
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 5
CORRECT TEXT
Upgrade the kernel, start the new kernel by default. kernel download from this address: ftp://server1.domain10.example.com/pub/update/new.kernel
Solution:
Download the new kernel file and then install it.
[root@desktop8 Desktop]# ls
kernel-2.6.32-71.7.1.el6.x86_64.rpm
kernel-firmware-2.6.32-71.7.1.el6.noarch.rpm
[root@desktop8 Desktop]# rpm -ivh kernel-*
Preparing... ###########################################
[100%]
1:kernel-firmware
########################################### [ 50%]
2:kernel
########################################### [100%]
Verify the grub.conf file, whether use the new kernel as the default boot. [root@desktop8 Desktop]# cat /boot/grub/grub.conf default=0
title Red Hat Enterprise Linux Server (2.6.32-71.7.1.el6.x86_64)
root (hd0,0)
kernel /vmlinuz-2.6.32-71.7.1.el6.x86_64 ro root=/dev/mapper/vol0-root
rd_LVM_LV=vol0/root rd_NO_LUKS rd_NO_MD
rd_NO_DM LANG=en_US.UTF-8 SYSFONT=latarcyrheb-sun16 KEYBOARDTYPE=pc
KEYTABLE=us crashkernel=auto rhgb quiet
initrd /initramfs-2.6.32-71.7.1.el6.x86_64.img
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 6
CORRECT TEXT
There is a local logical volumes in your system, named with shrink and belong to VGSRV volume group, mount to the /shrink directory. The definition of size is 320 MB.
Requirement:
Reduce the logical volume to 220 MB without any loss of data. The size is allowed between 200-260 MB after reducing.
Solution:
cd;umount /shrink
e2fsck -f /dev/mapper/vgsrv-shrink
resize2fs /dev/mapper/vgsrv-shrink 220M
lvreduce -L 220M /dev/mapper/vgsrv-shrink
mount -a
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 7
CORRECT TEXT
Configure your NFS services. Share the directory by the NFS Shared services.
Solution:
/etc/init.d/rpcbind start
/etc/init.d/nfslock start
/etc/init.d/nfs start
chkconfig rpcbind on
chkconfig nfslock on
chkconfig nfs on
showmount -e localhost
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 8
CORRECT TEXT
Part 1 (on Node1 Server)
Task 16 [Running Containers]
Configure your host journal to store all journal across reboot
Copy all journal files from /var/log/journal/ and put them in the /home/shangrila/container- logserver
Create and mount /home/shangrila/container-logserver as a persistent storage to the container as /var/log/ when container start
Solution:
*
[shangrila@node1 ~]$ podman ps
CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES
d5ffe018a53c registry.domain15.example.com:5000/rhel8/rsyslog:latest /bin/rsyslog.sh 5 seconds ago Up 4 seconds ago logserver
[shangrila@node1 ~]$ podman stats logserver
Error: stats is not supported in rootless mode without cgroups v2
[shangrila@node1 ~]$ podman stop logserver d5ffe018a53ca7eb075bf560d1f30822ab6fe51eba58fd1a8f370eda79806496
[shangrila@node1 ~]$ podman rm logserver
Error: no container with name or ID logserver found: no such container
[shangrila@node1 ~]$ mkdir -p container-journal/
*
[shangrila@node1 ~]$ sudo systemctl restart systemd-journald
[sudo] password for shangrila:
[shangrila@node1 ~]$ sudo cp -av /var/log/journal/* container-journal/
[shangrila@node1 ~]$ sudo cp -av /var/log/journal/* container-journal/
[shangrila@node1 ~]$ sudo chown -R shangrila container-journal/
[shangrila@node1 ~]$ podman run -d --name logserver -v /home/shangrila/container- journal/:/var/log/journal:Z registry.domain15.example.com:5000/rhel8/rsyslog [shangrila@node1 ~]$ podman ps
[shangrila@node1 ~]$ loginctl enable-linger
[shangrila@node1 ~]$ loginctl show-user shangrila|grep -i linger
Linger=yes
*
[shangrila@node1 ~]$ podman stop logserver
[shangrila@node1 ~]$ podman rm logserver
[shangrila@node1 ~]$ systemctl --user daemon-reload
[shangrila@node1 ~]$ systemctl --user enable --now container-logserver
[shangrila@node1 ~]$ podman ps
CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES
3903e1d09170 registry.domain15.example.com:5000/rhel8/rsyslog:latest /bin/rsyslog.sh 4
seconds ago Up 4 seconds ago logserver
[shangrila@node1 ~]$ systemctl --user stop container-logserver.service
*
[shangrila@node1 ~]$ sudo reboot
[shangrila@node1 ~]$ podman ps -a
CONTAINER ID IMAGE COMMAND CREATED STATUS PORTS NAMES
7e6cd59c506a registry.domain15.example.com:5000/rhel8/rsyslog:latest /bin/rsyslog.sh 10 seconds ago Up 9 seconds ago logserver
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 9
CORRECT TEXT
Configure your Host Name, IP Address, Gateway and DNS.
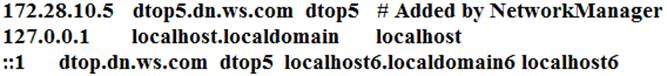
Host name: dtop5.dn.ws.com
IP Address: 172.28.10.5/4
Gateway: 172.28.10.1
DNS: 172.28.10.1
Solution:
✑ Configure Host Name
✑ vim /etc/sysconfig/network NETWORKING=yes HOSTNAME=dtop5.dn.ws.com GATEWAY=172.28.10.1
* 2. Configure IP Address, Gateway and DNS
Configure the network by Network Manager:
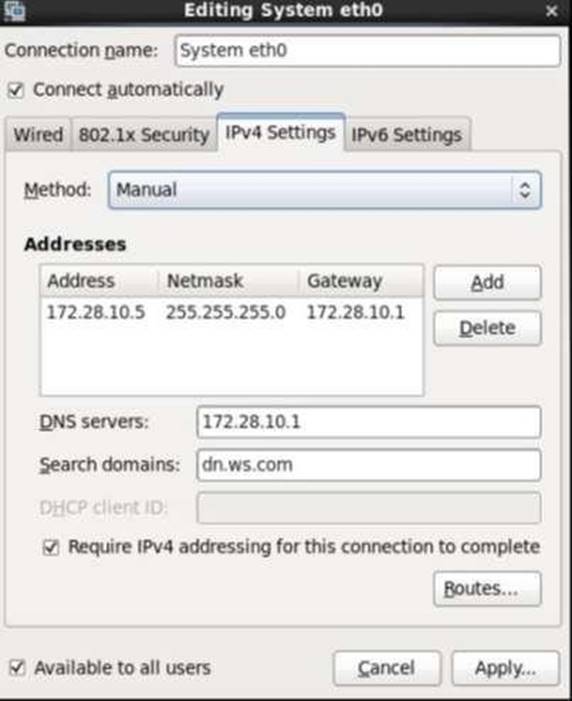
Note: Please remember to choose two options:
✑ Connect automatically
✑ Available to all users
Click "Apply", save and exit, and restart your network services:
# Service network restart
* 3. Validate these profiles:
a) Check gateway: # vim / etc / sysconfig / network
NETWORKING=yes
HOSTNAME=dtop5.dn.ws.com
GATEWAY=172.28.10.1
b) Check Host Name: # vim /etc/hosts
c) Check DNS: # vim /etc/resolv.conf
# Generated by NetworkManager
Search dn.ws.com
Nameserver 172.28.10.1
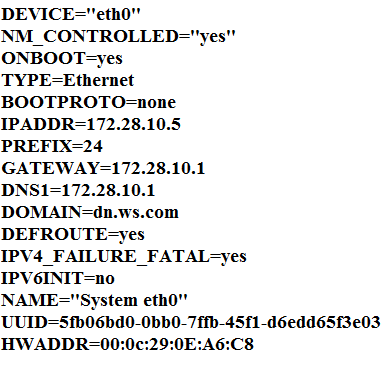
d) Check Gateway: # vim /etc/sysconfig/network-scripts/ifcfg-eth0
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 10
CORRECT TEXT
According the following requirements to create a local directory /common/admin.
✑ This directory has admin group.
✑ This directory has read, write and execute permissions for all admin group members.
✑ Other groups and users don’t have any permissions.
✑ All the documents or directories created in the/common/admin are automatically inherit the admin group.
Solution:
mkdir -p /common/admin
chgrp admin /common/admin
chmod 2770 /common/admin
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 11
CORRECT TEXT
Part 2 (on Node2 Server)
Task 4 [Managing Logical Volumes]
Resize the logical volume, lvrz and reduce filesystem to 4600 MiB. Make sure the the filesystem contents remain intact with mount point /datarz
(Note: partitions are seldom exactly the size requested, so anything within the range of 4200MiB to 4900MiB is acceptable)
Solution:
*
[root@node2 ~]# lsblk
NAME MAJ:MIN RM SIZE RO TYPE MOUNTPOINT
vdb 252:16 0 5G 0 disk
vdb1 252:17 0 4.2G 0 part
vgrz-lvrz 253:2 0 4.1G 0 lvm /datarz
vdc 252:32 0 5G 0 disk
vdc1 252:33 0 4.4G 0 part
datavg-datalv 253:3 0 3.9G 0 lvm /data
vdd 252:48 0 5G 0 disk
vde 252:64 0 10G 0 disk
[root@node2 ~]# lvs
LV VG Attr LSize Pool Origin Data% Meta% Move Log Cpy%Sync Convert
lvrz vgrz -wi-ao---- 4.10g
[root@node2 ~]# vgs
VG #PV #LV #SN Attr VSize VFree
vgrz 1 1 0 wz--n- <4.15g 48.00m
[root@node2 ~]# parted /dev/vdb print
Number Start End Size Type File system Flags
1 1049kB 4456MB 4455MB primary lvm
*
[root@node2 ~]# df -hT
Filesystem Type Size Used Avail Use% Mounted on
/dev/mapper/vgrz-lvrz ext4 4.0G 17M 3.8G 1% /datarz
[root@node2 ~]# parted /dev/vdb mkpart primary 4456MiB 5100MiB
[root@node2 ~]# parted /dev/vdb set 2 lvm on
[root@node2 ~]# udevadm settle
[root@node2 ~]# pvcreate /dev/vdb2
Physical volume "/dev/vdb2" successfully created.
*
[root@node2 ~]# vgextend vgrz /dev/vdb2
Volume group "vgrz" successfully extended
[root@node2 ~]# lvextend -r -L 4600M /dev/vgrz/lvrz
Size of logical volume vgrz/lvrz changed from 4.10 GiB (1050 extents) to 4.49 GiB (1150 extents).
Logical volume vgrz/lvrz successfully resized.
[root@node2 ~]# resize2fs /dev/vgrz/lvrz
[root@node2 ~]# df -hT
Filesystem Type Size Used Avail Use% Mounted on
/dev/mapper/vgrz-lvrz ext4 4.4G 17M 4.2G 1% /datarz
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 12
CORRECT TEXT
One Package named zsh is dump on ftp://server1.example.com under /pub/updates directory and your FTP server is 192.168.0.254. Install the package zsh.
Solution:
✑ rpm -ivh ftp://server1/example.com/pub/updates/zsh-* or
✑ Login to ftp server : ftp ftp://server1.example.com using anonymous user.
✑ Change the directory: cd pub and cd updates
✑ Download the package: mget zsh-*
✑ Quit from the ftp prompt : bye
✑ Install the package
✑ rpm -ivh zsh-*
✑ Verify either package is installed or not : rpm -q zsh
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 13
CORRECT TEXT
Create a volume group, and set 16M as a extends. And divided a volume group containing 50 extends on volume group lv, make it as ext4 file system, and mounted automatically under /mnt/data.
Solution:
# pvcreate /dev/sda7 /dev/sda8
# vgcreate -s 16M vg1 /dev/sda7 /dev/sda8
# lvcreate -l 50 -n lvm02
# mkfs.ext4 /dev/vg1/lvm02
# blkid /dev/vg1/lv1
# vim /etc/fstab
# mkdir -p /mnt/data
UUID=xxxxxxxx /mnt/data ext4 defaults 0 0
# vim /etc/fstab
# mount -a
# mount (Verify)
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 14
CORRECT TEXT
Part 1 (on Node1 Server)
Task 12 [Accessing Network-Attached Storage]
Configure autofs to automount the home directories of user remoteuserX. Note the following:
utility.domain15.example.com(172.25.15.9), NFS-exports /netdir to your system, where user is remoteuserX where X is your domain number
remoteuserX home directory is utility.domain15.example.com:/netdir/remoteuserX remoteuserX home directory should be auto mounted locally at /netdir as
/netdir/remoteuserX
Home directories must be writable by their users while you are able to login as any of the remoteuserX only home directory that is accessible from your system
Solution:
*
•
[root@host ~]#systemctl enable sssd.service
[root@host ~]#systemctl start sssg.service
[root@host ~]#getent passwd remoteuser15
[root@host ~]#yum install autofs
[root@host ~]#vim /etc/auto.master.d/home9.autofs
/netdir/remoteuser15 /etc/auto.home9
[root@host ~]#vim /etc/auto.home9
remoteuser15 –rw,sync utility.network15.example.com:/netdir/remoteuser15/&
[root@host ~]#systemctl enable autofs
[root@host ~]#systemctl restart autofs
[root@host ~]#su - remoteuser15
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 15
CORRECT TEXT
Configure autofs to automount the home directories of LDAP users as follows: host.domain11.example.com NFS-exports /home to your system.
This filesystem contains a pre-configured home directory for the user ldapuser11 ldapuser11's home directory is host.domain11.example.com /rhome/ldapuser11 ldapuser11's home directory should be automounted locally beneath /rhome as
/rhome/ldapuser11
Home directories must be writable by their users ldapuser11's password is 'password'.
Solution:
✑ vim /etc/auto.master /rhome /etc/auto.misc
wq!
# vim /etc/auto.misc
ldapuser11 --rw,sync host.domain11.example.com:/rhome/ldpauser11 :wq!
#service autofs restart
✑ service autofs reload
✑ chkconfig autofs on
✑ su -ldapuser11
Login ldapuser with home directory
# exit
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 16
CORRECT TEXT
Part 2 (on Node2 Server)
Task 3 [Managing Logical Volumes]
Create a new volume group in the name of datavg and physical volume extent is 16 MB Create a new logical volume in the name of datalv with the size of 250 extents and file
system must xfs
Then the logical volume should be mounted automatically mounted under /data at system boot time
Solution:
*
[root@node2 ~]# lsblk
NAME MAJ:MIN RM SIZE RO TYPE MOUNTPOINT
vdb 252:16 0 5G 0 disk
vdb1 252:17 0 4.2G 0 part
vgrz-lvrz 253:2 0 4.1G 0 lvm /datarz
vdc 252:32 0 5G 0 disk
vdd 252:48 0 5G 0 disk
vde 252:64 0 10G 0 disk
[root@node2 ~]# parted /dev/vdc mklabel msdos
[root@node2 ~]# parted /dev/vdc mkpart primary 1MiB 4200MiB
[root@node2 ~]# parted /dev/vdc set 1 lvm on
*
[root@node2 ~]# udevadm settle
[root@node2 ~]# pvcreate /dev/vdc1
Physical volume "/dev/vdc1" successfully created.
[root@node2 ~]# vgcreate -s 16M datavg /dev/vdc1
Volume group "datavg" successfully created
[root@node2 ~]# lvcreate -n datalv -L 4000M datavg
Logical volume "datalv" created.
[root@node2 ~]# mkfs.xfs /dev/datavg/datalv
[root@node2 ~]# mkdir /data
[root@node2 ~]# blkid
/dev/mapper/datavg-datalv: UUID="7397a292-d67d-4632-941e-382e2bd922ce"
BLOCK_SIZE="512" TYPE="xfs"
*
[root@node2 ~]# vim /etc/fstab
UUID=7397a292-d67d-4632-941e-382e2bd922ce /data xfs defaults 0 0
[root@node2 ~]# mount UUID=7397a292-d67d-4632-941e-382e2bd922ce /data
[root@node2 ~]# reboot
[root@node2 ~]# df -hT
Filesystem Type Size Used Avail Use% Mounted on
/dev/mapper/datavg-datalv xfs 3.9G 61M 3.9G 2% /data
Does this meet the goal?
- A. Yes
- B. Not Mastered
Answer: A
NEW QUESTION 17
......
P.S. Easily pass EX200 Exam with 136 Q&As Surepassexam Dumps & pdf Version, Welcome to Download the Newest Surepassexam EX200 Dumps: https://www.surepassexam.com/EX200-exam-dumps.html (136 New Questions)