The Regenerate Guide To CAS-004 Questions Pool
Real of CAS-004 practice exam materials and simulations for CompTIA certification for IT learners, Real Success Guaranteed with Updated CAS-004 pdf dumps vce Materials. 100% PASS CompTIA Advanced Security Practitioner (CASP+) Exam exam Today!
Free CAS-004 Demo Online For CompTIA Certifitcation:
NEW QUESTION 1
A web service provider has just taken on a very large contract that comes with requirements that are currently not being implemented in order to meet contractual requirements, the company must achieve the following thresholds
• 99 99% uptime
• Load time in 3 seconds
• Response time = <1 0 seconds
Starting with the computing environment, which of the following should a security engineer recommend to BEST meet the requirements? (Select THREE)
- A. Installing a firewall at corporate headquarters
- B. Deploying a content delivery network
- C. Implementing server clusters
- D. Employing bare-metal loading of applications
- E. Lowering storage input/output
- F. Implementing RAID on the backup servers
- G. Utilizing redundant power for all developer workstations
- H. Ensuring technological diversity on critical servers
Answer: BCE
Explanation:
To meet the contractual requirements of the web service provider, a security engineer should recommend the following actions:
✑ Deploying a content delivery network (CDN): A CDN is a distributed system of
servers that delivers web content to users based on their geographic location, the origin of the content, and the performance of the network. A CDN can help improve the uptime, load time, and response time of web services by caching content closer to the users, reducing latency and bandwidth consumption. A CDN can also help mitigate distributed denial-of-service (DDoS) attacks by absorbing or filtering malicious traffic before it reaches the origin servers, reducing the impact on the web service availability12.
✑ Implementing server clusters: A server cluster is a group of servers that work
together to provide high availability, scalability, and load balancing for web services. A server cluster can help improve the uptime, load time, and response time of web services by distributing the workload across multiple servers, reducing the risk of single points of failure and performance bottlenecks. A server cluster can also help recover from failures by automatically switching to another server in case of a malfunction34.
✑ Lowering storage input/output (I/O): Storage I/O is the amount of data that can be
read from or written to a storage device in a given time. Storage I/O can affect the performance of web services by limiting the speed of data transfer between the servers and the storage devices. Lowering storage I/O can help improve the load time and response time of web services by reducing the latency and congestion of data access. Lowering storage I/O can be achieved by using faster storage devices, such as solid-state drives (SSDs), optimizing the storage layout and configuration, such as using RAID or striping, and caching frequently accessed data in memory5 .
Installing a firewall at corporate headquarters is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. A firewall is a device or software that filters and blocks unwanted network traffic based on predefined rules. A firewall can help improve the security of web services by preventing unauthorized access and attacks, but it may also introduce additional latency and complexity to the network.
Employing bare-metal loading of applications is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Bare-metal loading is a technique that allows applications to run directly on hardware without an operating system or a hypervisor. Bare-metal loading can help improve the performance and efficiency of applications by eliminating the overhead and interference of other software layers, but it may also increase the difficulty and cost of deployment and maintenance.
Implementing RAID on the backup servers is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. RAID (redundant array of independent disks) is a technique that combines multiple disks into a logical unit that provides improved performance, reliability, or both. RAID can help improve the availability and security of backup data by protecting it from disk failures or corruption, but it may also introduce additional complexity and overhead to the backup process.
Utilizing redundant power for all developer workstations is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Redundant power is a technique that provides multiple sources of power for an IT system in case one fails. Redundant power can help improve the availability and reliability of developer workstations by preventing them from losing power due to outages or surges, but it may also increase the cost and energy consumption of the system.
Ensuring technological diversity on critical servers is not a recommended action to meet the contractual requirements, as it does not directly affect the uptime, load time, or response time of web services. Technological diversity is a technique that uses different types of hardware, software, or platforms in an IT environment. Technological diversity can help improve resilience by reducing single points of failure and increasing compatibility, but it may also introduce additional complexity and inconsistency to the
environment. References: What Is CDN? How Does CDN Work? | Imperva, What Is Server Clustering? | IBM, What Is Server Clustering? | IBM, Server Clustering: What It Is & How It Works | Liquid Web, Storage I/O Performance - an overview | ScienceDirect Topics, [How
to Improve Storage I/O Performance | StarWind Blog], [What Is Firewall Security? | Cisco], [What is Bare Metal? | IBM], [What is RAID? | Dell Technologies US], [What Is Redundant Power Supply? | Dell Technologies US], [Technological Diversity - an overview | ScienceDirect Topics]
NEW QUESTION 2
A security engineer needs 10 implement a CASB to secure employee user web traffic. A Key requirement is mat relevant event data must be collected from existing on-premises infrastructure components and consumed by me CASB to expand traffic visibility. The solution must be nighty resilient to network outages. Which of the following architectural components would BEST meet these requirements?
- A. Log collection
- B. Reverse proxy
- C. AWAF
- D. API mode
Answer: A
NEW QUESTION 3
A company is looking at sending historical backups containing customer PII to a cloud service provider to save on storage costs. Which of the following is the MOST important consideration before making this decision?
- A. Availability
- B. Data sovereignty
- C. Geography
- D. Vendor lock-in
Answer: B
NEW QUESTION 4
A client is adding scope to a project. Which of the following processes should be used when requesting updates or corrections to the client's systems?
- A. The implementation engineer requests direct approval from the systems engineer and the Chief Information Security Officer.
- B. The change control board must review and approve a submission.
- C. The information system security officer provides the systems engineer with the system updates.
- D. The security engineer asks the project manager to review the updates for the client's system.
Answer: B
Explanation:
The change control board (CCB) is a committee that consists of subject matter experts and managers who decide whether to implement proposed changes to a project. The change control board is part of the change management plan, which defines the roles and processes for managing change within a team or organization. The change control board must review and approve a submission for any change request that affects the scope, schedule, budget, quality, or risks of the project. The change control board evaluates the impact and benefits of the change request and decides whether to accept, reject, or defer it.
* A. The implementation engineer requesting direct approval from the systems engineer and the Chief Information Security Officer is not a correct process for requesting updates or corrections to the client’s systems, because it bypasses the change control board and the project manager. This could lead to unauthorized changes that could compromise the project’s objectives and deliverables.
* C. The information system security officer providing the systems engineer with the system updates is not a correct process for requesting updates or corrections to the client’s systems, because it does not involve the change control board or the project manager. This could lead to unauthorized changes that could introduce security vulnerabilities or conflicts with other system components.
* D. The security engineer asking the project manager to review the updates for the client’s system is not a correct process for requesting updates or corrections to the client’s systems, because it does not involve the change control board. The project manager is
responsible for facilitating the change management process, but not for approving or rejecting change requests.
https://www.projectmanager.com/blog/change-control-board-roles-responsibilities- processes
NEW QUESTION 5
An energy company is required to report the average pressure of natural gas used over the past quarter. A PLC sends data to a historian server that creates the required reports.
Which of the following historian server locations will allow the business to get the required reports in an and IT environment?
- A. In the environment, use a VPN from the IT environment into the environment.
- B. In the environment, allow IT traffic into the environment.
- C. In the IT environment, allow PLCs to send data from the environment to the IT environment.
- D. Use a screened subnet between the and IT environments.
Answer: D
Explanation:
A screened subnet is a network segment that separates two different environments, such as (operational technology) and IT (information technology), and provides security controls to limit and monitor the traffic between them. This would allow the business to get the required reports from the historian server without exposing the environment to unnecessary risks. Using a VPN, allowing IT traffic, or allowing PLCs to send data are less secure options that could compromise the environment. Verified References: https://www.comptia.org/blog/what-is-operational-technology https://partners.comptia.org/docs/default-source/resources/casp-content-guide
NEW QUESTION 6
Which of the following is the MOST important cloud-specific risk from the CSP’s viewpoint?
- A. Isolation control failure
- B. Management plane breach
- C. Insecure data deletion
- D. Resource exhaustion
Answer: B
NEW QUESTION 7
An attacker infiltrated the code base of a hardware manufacturer and inserted malware before the code was compiled. The malicious code is now running at the hardware level across a number of industries and sectors. Which of the following categories BEST describes this type of vendor risk?
- A. SDLC attack
- B. Side-load attack
- C. Remote code signing
- D. Supply chain attack
Answer: D
NEW QUESTION 8
Which of the following terms refers to the delivery of encryption keys to a CASB or a third- party entity?
- A. Key sharing
- B. Key distribution
- C. Key recovery
- D. Key escrow
Answer: D
Explanation:
Key escrow is a process that involves storing encryption keys with a trusted third party, such as a CASB (Cloud Access Security Broker) or a government agency. Key escrow can enable authorized access to encrypted data in case of emergencies, legal issues, or data recovery. However, key escrow also introduces some risks and challenges, such as trust, security, and privacy. References: https://www.techopedia.com/definition/1772/key-escrow https://searchsecurity.techtarget.com/definition/key-escrow
NEW QUESTION 9
Which of the following are risks associated with vendor lock-in? (Choose two.)
- A. The client can seamlessly move data.
- B. The vendor can change product offerings.
- C. The client receives a sufficient level of service.
- D. The client experiences decreased quality of service.
- E. The client can leverage a multicloud approach.
- F. The client experiences increased interoperability.
Answer: BD
Explanation:
Reference: https://www.cloudflare.com/learning/cloud/what-is-vendor-lock- in/#:~:text=Vendor%20lock%2Din%20can%20become,may%20involve%20reformatting%2 0the%20data
Vendor lock-in is a situation where a client becomes dependent on a vendor for products or services and cannot easily switch to another vendor without substantial costs or inconvenience. Some of the risks associated with vendor lock-in are that the vendor can change product offerings, such as by discontinuing or modifying features, increasing prices, or reducing support, and that the client experiences decreased quality of service, such as by having poor performance, reliability, or security. These risks could affect the client’s business operations, satisfaction, or competitiveness. The client can seamlessly move data, the client receives a sufficient level of service, and the client can leverage a multicloud approach are not risks associated with vendor lock-in, but potential benefits of avoiding vendor lock-in. Verified References: https://www.comptia.org/blog/what-is-vendor- lock-in https://partners.comptia.org/docs/default-source/resources/casp-content-guide
NEW QUESTION 10
A Chief Security Officer (CSO) is concerned about the number of successful ransomware attacks that have hit the company. The data Indicates most of the attacks came through a
fake email. The company has added training, and the CSO now wants to evaluate whether the training has been successful. Which of the following should the CSO implement?
- A. Simulating a spam campaign
- B. Conducting a sanctioned vishing attack
- C. Performing a risk assessment
- D. Executing a penetration test
Answer: A
Explanation:
A spam campaign is a mass distribution of unsolicited or fraudulent emails that may contain malicious links, attachments, or requests. Spam campaigns are often used by attackers to deliver ransomware, which is a type of malware that encrypts the victim’s data and demands a ransom for its decryption.
Simulating a spam campaign would allow the Chief Security Officer (CSO) to evaluate whether the training has been successful in reducing the number of successful ransomware attacks that have hit the company, because it would:
✑ Test the employees’ ability to recognize and avoid clicking on fake or malicious
emails, which is one of the main vectors for ransomware infection.
✑ Measure the effectiveness of the training by comparing the click-through rate and the infection rate before and after the training.
✑ Provide feedback and reinforcement to the employees by informing them of their performance and reminding them of the best practices for email security.
NEW QUESTION 11
A major broadcasting company that requires continuous availability to streaming content needs to be resilient against DDoS attacks Which of the following is the MOST important infrastructure security design element to prevent an outage7
- A. Supporting heterogeneous architecture
- B. Leveraging content delivery network across multiple regions
- C. Ensuring cloud autoscaling is in place
- D. Scaling horizontally to handle increases in traffic
Answer: B
Explanation:
A content delivery network (CDN) is a distributed system of servers that delivers web content to users based on their geographic location, the origin of the content, and the performance of the network. A CDN can help improve the availability and performance of web applications by caching content closer to the users, reducing latency and bandwidth consumption. A CDN can also help mitigate distributed denial-of-service (DDoS) attacks by absorbing or filtering malicious traffic before it reaches the origin servers, reducing the impact on the application availability. Supporting heterogeneous architecture means using different types of hardware, software, or platforms in an IT environment. This can help improve resilience by reducing single points of failure and increasing compatibility, but it does not directly prevent DDoS attacks. Ensuring cloud autoscaling is in place means using cloud services that automatically adjust the amount of resources allocated to an application based on the demand or load. This can help improve scalability and performance by providing more resources when needed, but it does not directly prevent
DDoS attacks. Scaling horizontally means adding more servers or nodes to an IT environment to increase its capacity or throughput. This can help improve scalability and performance by distributing the load across multiple servers, but it does not directly prevent DDoS attacks. References: [CompTIA Advanced Security Practitioner (CASP+) Certification Exam Objectives], Domain 2: Enterprise Security Architecture, Objective 2.4: Select controls based on systems security evaluation models
NEW QUESTION 12
A technician is reviewing the logs and notices a large number of files were transferred to remote sites over the course of three months. This activity then stopped. The files were transferred via TLS-protected HTTP sessions from systems that do not send traffic to those sites.
The technician will define this threat as:
- A. a decrypting RSA using obsolete and weakened encryption attack.
- B. a zero-day attack.
- C. an advanced persistent threat.
- D. an on-path attack.
Answer: C
Explanation:
Reference: https://www.internetsociety.org/deploy360/tls/basics/
An advanced persistent threat (APT) is a type of cyberattack that involves a stealthy and continuous process of compromising and exploiting a target system or network. An APT typically has a specific goal or objective, such as stealing sensitive data, disrupting operations, or sabotaging infrastructure. An APT can use various techniques to evade detection and maintain persistence, such as encryption, proxy servers, malware, etc. The scenario described in the question matches the characteristics of an APT. References: https://www.cisco.com/c/en/us/products/security/what-is-apt.html https://www.imperva.com/learn/application-security/advanced-persistent-threat-apt/
NEW QUESTION 13
A Chief information Security Officer (CISO) has launched to create a rebuts BCP/DR plan for the entire company. As part of the initiative , the security team must gather data supporting s operational importance for the applications used by the business and determine the order in which the application must be back online. Which of the following be the FIRST step taken by the team?
- A. Perform a review of all policies an procedures related to BGP a and DR and created an educated educational module that can be assigned to at employees to provide training on BCP/DR events.
- B. Create an SLA for each application that states when the application will come back online and distribute this information to the business units.
- C. Have each business unit conduct a BIA and categories the application according to the cumulative data gathered.
- D. Implement replication of all servers and application data to back up detacenters that are geographically from the central datacenter and release an upload BPA to all clients.
Answer: C
NEW QUESTION 14
A security researcher detonated some malware in a lab environment and identified the following commands running from the EDR tool: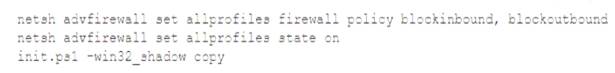
With which of the following MITRE ATT&CK TTPs is the command associated? (Select TWO).
- A. Indirect command execution
- B. OS credential dumping
- C. Inhibit system recovery
- D. External remote services
- E. System information discovery
- F. Network denial of service
Answer: BE
Explanation:
OS credential dumping is the process of obtaining account login and password information, normally in the form of a hash or a clear text password, from the operating system and software. System information discovery is the process of gathering information about the system, such as hostname, IP address, OS version, running processes, etc. Both of these techniques are commonly used by adversaries to gain access to sensitive data and resources on the target system. The command shown in the image is using Mimikatz, a tool that can dump credentials from memory, and also querying the system information using WMIC. Verified References: https://attack.mitre.org/techniques/T1003/
 https://attack.mitre.org/techniques/T1082/ https://github.com/gentilkiwi/mimikatz https://docs.microsoft.com/en-us/windows/win32/wmisdk/wmic
NEW QUESTION 15
A cybersecurity analyst discovered a private key that could have been exposed.
Which of the following is the BEST way for the analyst to determine if the key has been compromised?
- A. HSTS
- B. CRL
- C. CSRs
- D. OCSP
Answer: C
Explanation:
Reference: https://www.ssl.com/faqs/compromised-private-keys/
NEW QUESTION 16
A security architect recommends replacing the company’s monolithic software application with a containerized solution. Historically, secrets have been stored in the application's configuration files. Which of the following changes should the security architect make in the new system?
- A. Use a secrets management tool.
- B. ‘Save secrets in key escrow.
- C. Store the secrets inside the Dockerfiles.
- D. Run all Dockerfles in a randomized namespac
Answer: A
Explanation:
A secrets management tool is a tool that helps companies securely store, transmit, and manage sensitive digital authentication credentials such as passwords, keys, tokens, certificates, and other secrets. A secrets management tool can help prevent secrets sprawl, enforce business policies, and inject secrets into pipelines. A secrets management tool can also help protect secrets from unauthorized access, leakage, or compromise by using encryption, tokenization, access control, auditing, and rotation. A secrets management tool is a recommended solution for replacing the company’s monolithic software application with a containerized solution, because it can provide a centralized and consistent way to manage secrets across multiple containers and environments.
* B. Saving secrets in key escrow is not a recommended solution for replacing the company’s monolithic software application with a containerized solution, because it does not address the operational challenges of managing secrets for containers. Key escrow is a process of storing cryptographic keys with a trusted third party that can release them under certain conditions. Key escrow can be useful for backup or recovery purposes, but it does not provide the same level of security and automation as a secrets management tool.
* C. Storing the secrets inside the Dockerfiles is not a recommended solution for replacing the company’s monolithic software application with a containerized solution, because it exposes the secrets to anyone who can access the Dockerfiles or the images built from them. Storing secrets inside the Dockerfiles is equivalent to hardcoding them into the application code, which is a bad practice that violates the principle of least privilege and increases the risk of secrets leakage or compromise.
* D. Running all Dockerfiles in a randomized namespace is not a recommended solution for replacing the company’s monolithic software application with a containerized solution, because it does not address the issue of storing and managing secrets for containers. Running Dockerfiles in a randomized namespace is a technique to avoid name conflicts and collisions between containers, but it does not provide any security benefits for secrets.
NEW QUESTION 17
An organization is assessing the security posture of a new SaaS CRM system that handles sensitive PI I and identity information, such as passport numbers. The SaaS CRM system does not meet the organization's current security standards. The assessment identifies the following:
1) There will be a 520,000 per day revenue loss for each day the system is delayed going into production.
2) The inherent risk is high.
3) The residual risk is low.
4) There will be a staged deployment to the solution rollout to the contact center. Which of the following risk-handling techniques will BEST meet the organization's
requirements?
- A. Apply for a security exemption, as the risk is too high to accept.
- B. Transfer the risk to the SaaS CRM vendor, as the organization is using a cloud service.
- C. Accept the risk, as compensating controls have been implemented to manage the risk.
- D. Avoid the risk by accepting the shared responsibility model with the SaaS CRM provider.
Answer: D
NEW QUESTION 18
A software development company makes Its software version available to customers from a web portal. On several occasions, hackers were able to access the software repository to change the package that is automatically published on the website. Which of the following would be the BEST technique to ensure the software the users download is the official software released by the company?
- A. Distribute the software via a third-party repository.
- B. Close the web repository and deliver the software via email.
- C. Email the software link to all customers.
- D. Display the SHA checksum on the website.
Answer: D
NEW QUESTION 19
A security analyst observes the following while looking through network traffic in a company's cloud log: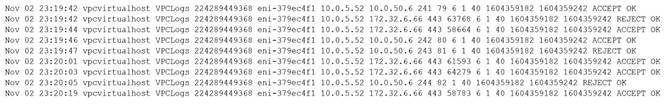
Which of the following steps should the security analyst take FIRST?
- A. Quarantine 10.0.5.52 and run a malware scan against the host.
- B. Access 10.0.5.52 via EDR and identify processes that have network connections.
- C. Isolate 10.0.50.6 via security groups.
- D. Investigate web logs on 10.0.50.6 to determine if this is normal traffic.
Answer: D
NEW QUESTION 20
......
100% Valid and Newest Version CAS-004 Questions & Answers shared by Allfreedumps.com, Get Full Dumps HERE: https://www.allfreedumps.com/CAS-004-dumps.html (New 553 Q&As)